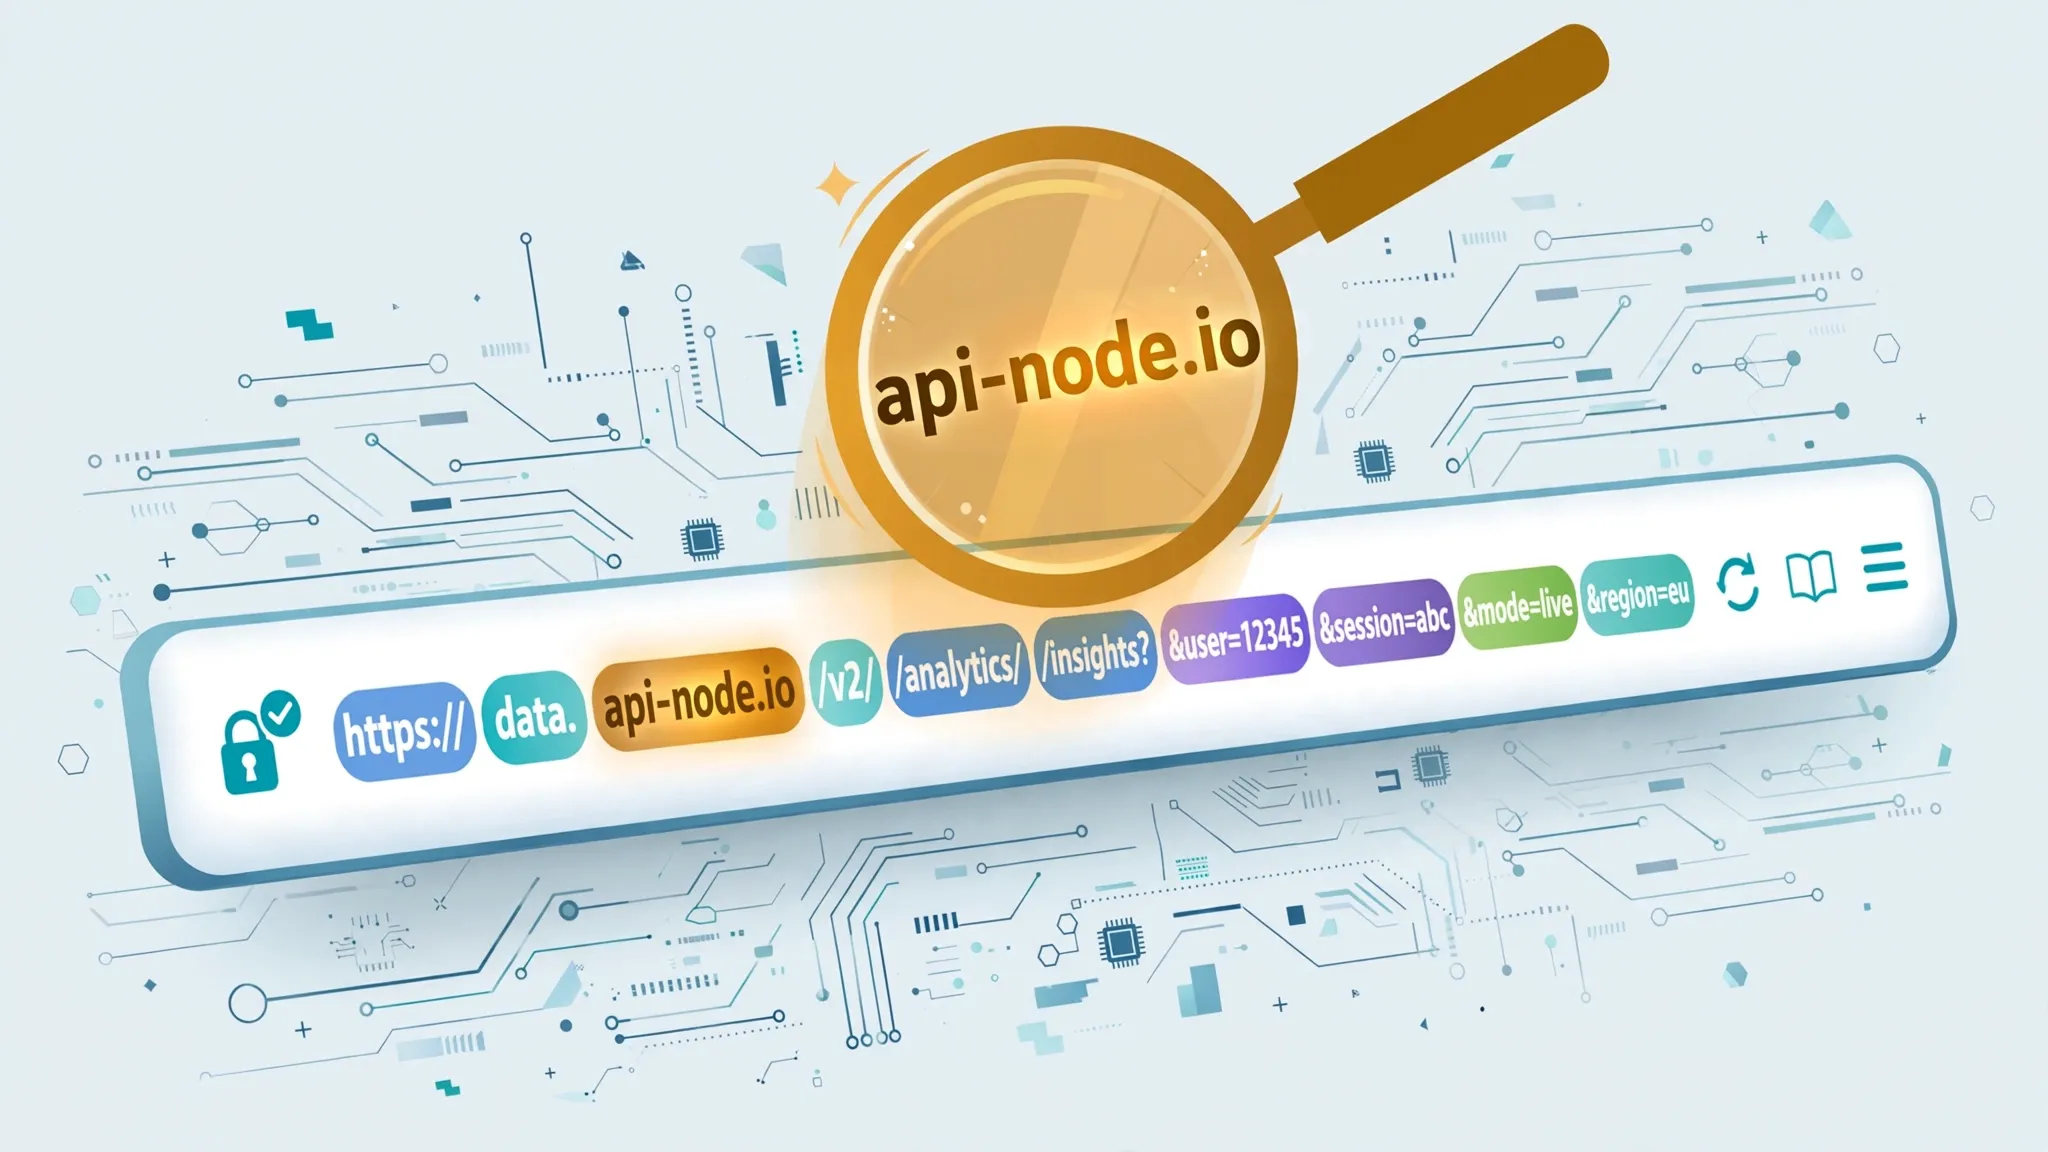
You’ve seen links like this one, probably in a newsletter or a shared chat: https://www.example-shop.com/sale/shoes?utm_source=newsletter&utm_medium=email&utm_campaign=autumn-sale#deals. It looks like someone fell asleep on the keyboard. But almost every character in there is doing a job — and once you can see the jobs, a long address becomes readable. More importantly, it becomes harder to fool you.

A web address (URL) is built from a small set of parts, in the same order, every time. You don’t need to memorise the technical names. You need to know which part says who you’re talking to, which part is the site talking to itself, and which part scammers are counting on you never looking at.
Every address has the same three big pieces
Take a short one first: https://superdova.com/internet-guides.
The beginning — https:// — sets the rules of the conversation. It says which protocol the browser should use to talk to the site. https means the connection is encrypted; http (without the s) means it isn’t. These days browsers will flat-out warn you before loading a plain http page, which is why you rarely see it. Either way, this part tells you nothing about whether the site itself is honest — the padlock icon alone doesn’t prove a site is trustworthy, and plenty of scam pages run on encrypted https connections.
The middle — superdova.com — is the domain: who you’re actually visiting. This is the most important part of the whole address, and the rest of this article keeps coming back to it.
The tail — /internet-guides — is the path: where on that site you’re going. Think of the domain as the building and the path as the room number. Paths are readable by design: /internet-guides is a section of the site, /2026/09/29/some-article would be an article filed by date. Nothing here is a secret.
The domain is the part scammers hope you’ll skip
The single most useful trick in this article: when you’re checking an address, find the domain by reading backwards from the first single slash.
Compare these two: support.apple.com/login and apple.support-center.example.com/login. In the first, everything before the slash reads support.apple.com — that’s Apple’s domain with a support prefix (a subdomain), and it’s genuinely Apple. In the second, reading back from the slash gives you apple.support-center.example.com — and the registered domain there is support-center.example.com. The word “apple” is just a decoration somebody stuck on the front. The real owner is whoever registered example.com, and that’s who would receive your login details.
This is the oldest phishing trick in the book, and it still works because it exploits a habit: glancing at the address and recognising a brand name anywhere in it. The brand name can sit in the subdomain, the path, even the query string — none of those mean the site belongs to the brand. Only the registered domain matters.
Two more tells worth knowing. First, scam domains lean on lookalikes: swapped letters, hyphens and extra words that the real domain doesn’t have — yourbank-secure-login.com is not your bank, however official the page looks. Second, your browser is already trying to help: Chrome will now flag a “Did you mean [site name]?” or “Fake site ahead” warning when an address is suspiciously close to a site you actually visit, because a URL that is slightly changed from a known safe site is a classic deception (Google’s own Chrome help pages document this behaviour). If the browser says it looks odd, believe the browser over the page.
Everything after the question mark is the site talking to itself
Now the messy half. In that example address from the start, everything after the ? is the query string: a set of key-value notes the page uses to do its job. ?q=shoes is a search term. ?page=2&sort=price-low is a filter. When you tick boxes on a shopping filter, those choices often show up right there in the address. Nothing sinister — it’s the site remembering what you asked for.
The bits that make links look like alphabet soup are usually tracking parameters, and the most common ones start with utm_. utm_source=newsletter tells the site’s analytics that you arrived from a newsletter; utm_campaign=autumn-sale says which campaign. They describe how you got there, not where you’re going — and they’re one more way your browsing gets tracked online. A useful party trick: you can delete everything from the ? onward (or just from ?utm_) and the page will almost always still load. The page doesn’t need them; the marketing department does.
The last two oddities, quickly. %20 and its percent-number friends are just percent-encoding: how addresses smuggle characters they can’t legally contain. %20 is a space, so my%20photo.jpg is just “my photo.jpg”. Safe to ignore. And a # near the end (like #deals) is a fragment: an instruction to your browser to scroll to a section of the page. Your browser handles it locally — it’s never even sent to the website.
A four-second habit before you click anything
Here’s the practical version of everything above, in the order your hands can actually do it.
On a computer, hover. Rest your cursor on a link in an email or message and the real address appears, usually in the bottom-left corner. The link text can say anything — “Reset your password now” — but the address it points to is the truth. Read the domain backwards from the first slash.
On a phone, long-press. Hold the link and the preview shows the full address before you commit. Read the domain first; the rest can wait.
Treat shortened links as wrapped parcels. A link like bit.ly/3xYz9Q hides the domain entirely, which is exactly the information you need. On a phone, long-press preview or paste it into a link-expander first — and the same goes for QR codes, which hide the address completely until your camera app shows you where it’s going.
When the address bar is truncated, tap it. Phone browsers often show only the domain and hide the rest. Tap the address bar to see the full thing before typing in a password.
Reading an address won’t turn you into a security analyst, and it was never meant to. It was meant to be the cheapest safety check on the internet: four seconds, no tools, no expertise. Scammers build entire operations around the assumption that nobody looks. Be the person who looks.