



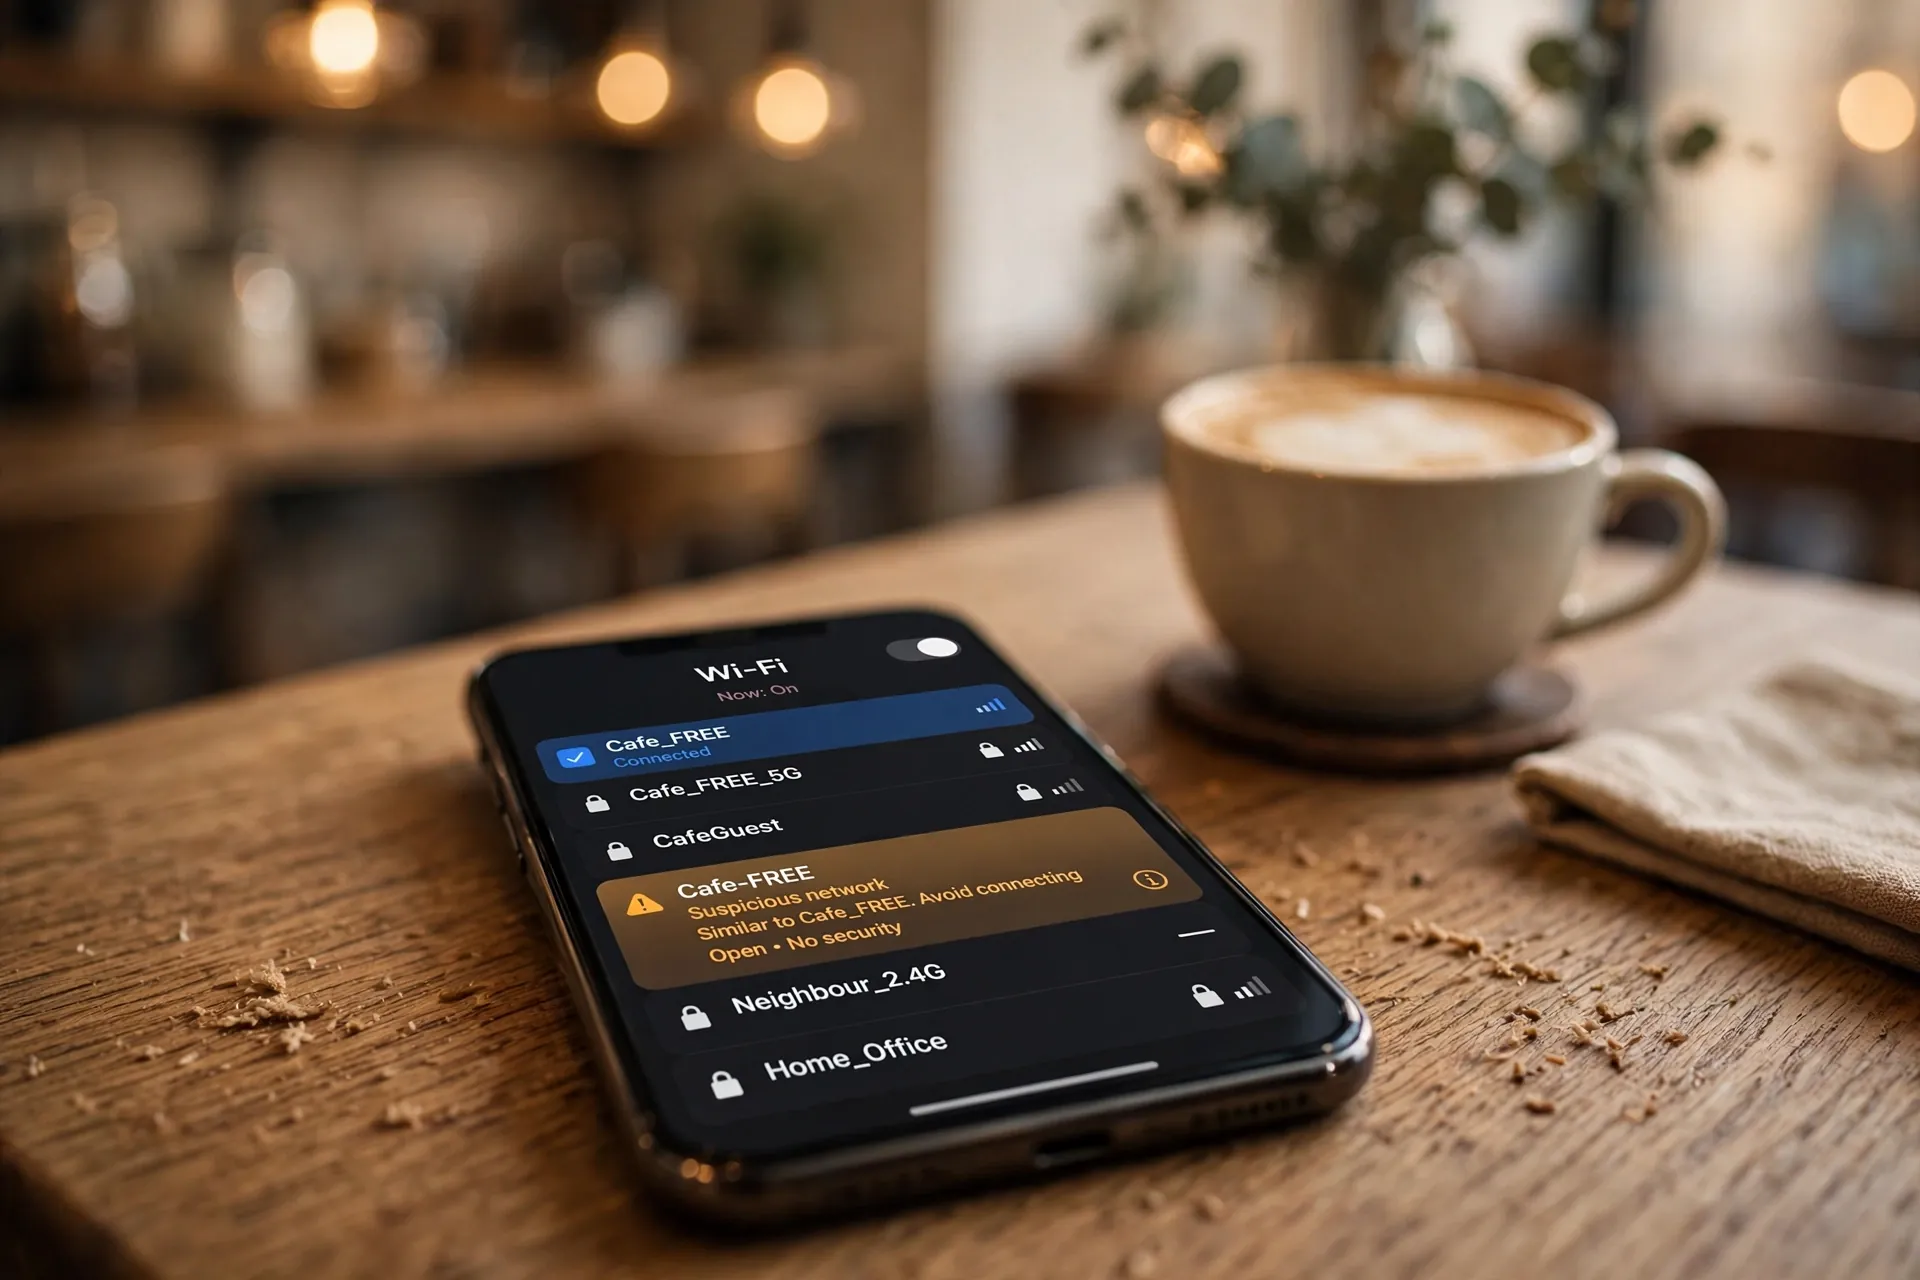
You’re sitting at the airport, waiting on a delayed flight, and your phone offers you a dozen networks: “Airport_Free_WiFi”, “Airport_Free_Wifi”, “AirportFreeWiFi”, one of them with a slightly different spelling than the others. Ten years of security advice is screaming at you: don’t touch any of them.

Here’s the honest version of that advice in 2026: the blanket panic is outdated. Your browser now encrypts far more of your traffic than it used to, and that’s changed what public Wi-Fi can actually expose. But a few real risks remain, and they’re worth understanding — because they’re the ones the old advice never quite explained.
What changed: the web quietly encrypted itself
Years ago, much of the web travelled in the open. On a shared network, someone with modest technical skill could potentially watch the unencrypted traffic of other users. That was the world the “never use public Wi-Fi” warnings were written for.
Today, the overwhelming majority of sites you use — banks, email, social media, shopping — use HTTPS, the encrypted connection marked by the padlock in your address bar. That encryption runs between your device and the website itself, so someone on the same café network can’t read the contents of your session. The network operator can still see which websites you visit — similar to what your internet provider can see about your browsing — but not the specific pages, messages, or passwords inside those visits.
One caveat worth remembering: the padlock only means the connection is encrypted, not that the site is trustworthy. A convincing phishing page can carry a padlock too — here’s what the padlock actually tells you.
So casual browsing on public Wi-Fi — maps, news, checking a booking — is far less exposed than it once was. The U.S. Federal Trade Commission still advises treating unsecured hotspots with caution, but its modern guidance centers on sensible habits rather than total avoidance.
The risks that didn’t go away
A network name can be copied by anyone
This is the one that matters most. Nothing stops a stranger from creating a hotspot called exactly what the coffee shop’s real one is called. Connect to the fake one, and your traffic runs through their equipment first. The FTC’s long-standing advice holds: confirm the exact network name with staff before connecting, and be suspicious if a network you’ve never seen before behaves like one you’ve used — especially if it suddenly asks for login credentials it never asked for before.
The login page itself can be the trap
Many public networks show a captive portal — the “enter your email / accept terms” page that appears before you get internet access. The real one is annoying but harmless. A fake one can be designed to harvest credentials. Rule of thumb: never enter a password you’d care about losing into a Wi-Fi login page. A hotel asking for your room number is one thing; a network asking for your email account password is a reason to walk away.
A password on the network isn’t proof of safety
An open network with no password is, as the FTC puts it plainly, not secure — treat it as if anyone can observe it. But don’t take a password as proof of safety either. Everyone in the coffee shop shares that password, and a fake network can require one too. Password protection keeps casual passers-by out; it says nothing about who else is on the network with you.
Some sites still aren’t encrypted
Most are, but not all — and modern browsers flag unencrypted pages with a warning. If your browser says a connection “is not secure,” believe it, especially on public Wi-Fi. Log out of the site if you end up on an unencrypted page mid-session; the FTC specifically advises ending the visit rather than continuing.
Two minutes of setup before you travel
These are one-time settings that make public networks considerably less risky.
Turn off auto-join for public networks. Phones love to reconnect to networks they’ve seen before — which is exactly how a lookalike network catches people. On iPhone, go to Settings → Wi-Fi, tap the ⓘ next to a public network, and switch off Auto-Join. You can also audit everything your phone remembers under Settings → Wi-Fi → Edit. On Android, open the network’s settings (the gear icon) and turn off its auto-reconnect option — Samsung phones label it “Auto reconnect”; the wording varies a little on other Android phones, but the toggle is in the same place.
Leave the private Wi-Fi address on. Your phone has a hardware identifier (a MAC address) it hands to every network it joins. Both iPhone and Android now use a randomized private address per network instead, which stops different venues from tracking your device across visits. It’s on by default — on iPhone you’ll find it under Settings → Wi-Fi → the ⓘ → Private Wi-Fi Address, and on Android under the network’s Privacy settings as “Use randomized MAC.” Just check that it hasn’t been switched off.
Update before you leave. Operating system and browser updates patch the very flaws that public-network attacks tend to exploit. The FTC lists keeping your browser and security software current among its core Wi-Fi safety tips. Run your updates at home, on your own network, before the trip.
While you’re connected
Use mobile data for anything that truly matters. CISA’s travel guidance is direct: avoid banking and shopping on public Wi-Fi, and use your cellular connection instead. For sensitive tasks, your phone’s personal hotspot removes the public network from the equation entirely. It’s the simplest upgrade available, and it costs you nothing extra.
Log out of accounts when you’re done. Don’t leave banking, email, or shopping sessions permanently signed in on a device you’ve used on a public network — sign out when you finish. Another piece of FTC advice that’s still current: don’t reuse the same password across sites, because one exposed credential then opens many doors.
Consider a VPN if you’re a regular. If public Wi-Fi is a daily part of your life — commuting, working from cafés — a reputable VPN encrypts everything between your device and the VPN provider, closing the gaps that HTTPS alone leaves. It’s one of the few cases where a VPN genuinely earns its keep.
Don’t override browser warnings. Browsers now flag fraudulent sites and unsafe connections. On a public network, where fake login pages and lookalike sites are the main remaining threat, that warning is the last line of defence. Never click through it just because you need the internet quickly.
Afterwards: forget the network
Once you’re done with a public network, remove it from your phone so it can’t silently reconnect later. On iPhone: Settings → Wi-Fi → Edit, and delete the network. On Android: tap the network and choose Forget. It takes ten seconds, and it closes the quietest hole of all — your phone auto-joining a network whose name an attacker can recreate tomorrow.
Public Wi-Fi doesn’t need to be feared, and it doesn’t need to be avoided entirely. The realistic posture is simpler than the old warnings made it sound: let encryption do its job, verify what you connect to, keep your device’s own defences switched on, and use your mobile data for the things that actually matter. Most of the time, that’s the whole of it.











Comments 1